Chinese developer of the ARTEX AI agent makes it closed-source after cyberattacks on South Korean banks
IA en un minuto newsroom · Editor: Jon Elgezabal
In 30 seconds
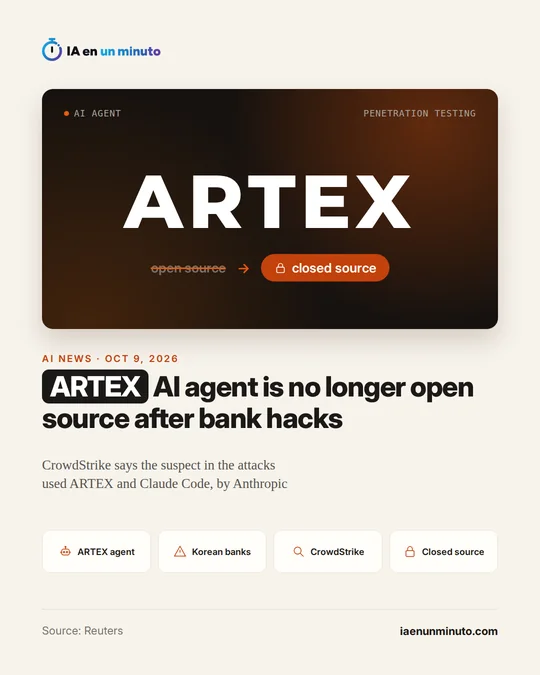
ARTEX, a Chinese AI agent for penetration testing, is no longer open source: its creator announced on GitHub that new versions and maintenance are over too. The move follows CrowdStrike naming it as a tool in the cyberattacks on South Korean banks, alongside Claude Code. The author of the program rejects any illegal use, and South Korean police are already investigating the attacks.
The Chinese developer of ARTEX, an open-source AI agent for security testing, said on Thursday, October 8, that it is being converted into a closed-source project, after cybersecurity firms identified it as a tool used in the recent cyberattack campaign against South Korean banks. The news comes from a Reuters dispatch published by The Hindu.
The developer, who uses the handle "Autumn-27" on GitHub, the code-hosting platform, wrote there that, given the misuse of the tool, the project will no longer be updated, no further versions will be released to the public and no maintenance support will be provided. The developer added that ARTEX was created to help enterprises and organizations run security risk tests and improve their security, expressed opposition to any illegal use of the software and disclaimed responsibility for conduct that violates laws and regulations. The statement did not explicitly address the attacks on South Korean banks. According to checks by Reuters, the ARTEX page on GitHub has been taken down.
ARTEX was released on GitHub this year. It automates penetration testing (the tests that look for vulnerabilities in the networks of an organization). It is not a large language model in its own right: it connects to external models such as ChatGPT, Claude and DeepSeek.
On Wednesday, October 7, American cybersecurity firm CrowdStrike said, according to Reuters, that the suspect behind the attacks, which were aimed at stealing customers' personal data, was likely a China-based 26-year-old who used ARTEX and Claude Code, the Anthropic tool. The CrowdStrike report adds caveats: it does not attribute the campaign to any named group and assesses, with moderate confidence, that the operator is likely a Chinese speaker and financially motivated. The age comes from personal details that someone included when asking Claude to write a security researcher résumé; the firm believes they likely belong to the attacker but says the available information cannot definitively tie them to that person.
According to that report, the campaign was active from late September to early October and resulted in exfiltrated data. On servers controlled by the attacker, researchers found open directories holding Claude Code session histories, ARTEX configuration files and Claude memory files. The ARTEX instance used DeepSeek v4.1-flash as its primary model, and the attacker also turned to GLM-5.3, from Zhipu AI, and Grok 4.6 in additional Claude Code sessions. The attacker also asked Claude where stolen Korean data is typically sold and for help finding Korean Telegram groups that sell data.
Since late September, at least nine South Korean banks have disclosed cyberattacks or been reported by local media as targets, according to Reuters. CrowdStrike, citing industry reports, refers to several financial organizations and notes that the number affected remains unconfirmed; according to those reports, at one bank the attacker breached a loan progress inquiry service used by financial brokers, and at another, a mobile work-support system for employees. South Korean police launched an investigation in the week of October 5, and President Lee Jae Myung called for robust response measures.
Mao Ning, spokesperson for the Chinese foreign ministry, told a regular press briefing on Thursday that the ministry was not familiar with the case and that China consistently opposes and combats hacking activities.
Why it matters · analysis and opinion
Closing the code comes too late for what already happened: what was published in the open could be downloaded, and the withdrawal only cuts off future versions and maintenance. The case teaches something more uncomfortable. Tools that automate penetration testing serve whoever defends a network just as well as whoever wants to break into it, and connected to language models they let a single person attack several organizations within a few weeks, as CrowdStrike describes. For a company, the practical reading is twofold. Flaws that used to take time to find are now located quickly, so internet-facing services, especially those used by outside partners and by employees on their phones, deserve a review of their own before someone else carries it out. And anyone using agents of this kind to audit themselves should know who maintains them.
Source: The Hindu (Reuters) · Written with the help of AI: how we make the news