curl 8.23.0 fixes an HTTP/2 vulnerability found with help from Claude
IA en un minuto newsroom · Editor: Jon Elgezabal
In 30 seconds
Anthropic, relying on Claude, came across a memory bug in curl that is triggered when sending data over HTTP/2 and that version 8.23.0 already fixes. A malicious server could use it to run code, though only by meeting many hard requirements, which is why curl keeps it at high severity. Versions 8.12.0 through 8.22.0 are exposed, and the advice is to upgrade, patch or do without HTTP/2.
curl, the open source tool for sending and downloading data over the internet, released version 8.23.0 on Wednesday, October 14, with 24 vulnerabilities fixed. Anthropic discovered one of them with help from Claude.
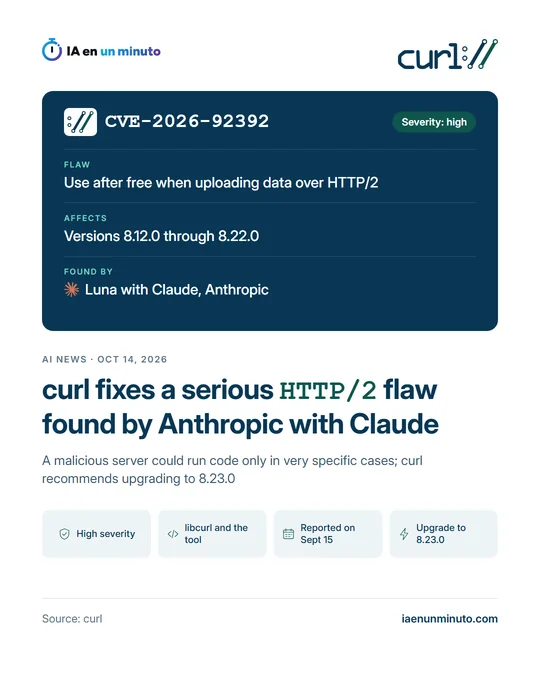
It is CVE-2026-92392, a "use after free" flaw (the program keeps using a piece of memory it had already released) that shows up when uploading data over HTTP/2, the protocol that carries several transfers at once over a single connection. curl gives it high severity, and Daniel Stenberg, of curl, writes on his blog that it ranks among the worst curl vulnerabilities in a long time.
According to Stenberg, the problem arises when the server halts the upload, sends back part of the response and cancels that transfer without closing the connection: curl treats it as finished but holds on to a reference to memory that the application frees later.
The curl advisory explains that a malicious server has been shown to be able to turn the flaw into remote code execution, but only if many very specific conditions all hold. The victim has to upload data to that server, whose certificate must be valid, at a size of roughly 135 KB, and the attacker needs exact details of the victim's system, such as its architecture and curl version. Because the curl team sees those conditions as extremely hard to meet in practice, it rated the flaw high rather than critical. Stenberg adds that an attack attempt would most likely only make the program crash and that the odds of success are slim.
Affected versions run from 8.12.0 to 8.22.0, in both libcurl, the library that many applications use without always saying so, and the command line tool. Other branches also have fixed versions: 8.20.2, 8.16.2 and 8.14.3. curl recommends upgrading to 8.23.0, applying the patch to the version in use or not using HTTP/2. The patch is by Stefan Eissing.
The advisory credits the discovery to "Luna with Claude, Anthropic". According to Stenberg, it was found by Luna Tong, of Anthropic, with OSS Scanner, the company's new scanner for open source code, which he assumes uses its AI models. It was reported on September 15, curl's security team confirmed it within a few hours and brought the next version forward: the cycle went from eight to six weeks.
Stenberg points out that libcurl is written in C, a language that does not protect memory, and that with one that did the mistake would probably have been avoided. Even so, he rules out rewriting curl in another language, such as Rust.
Why it matters · analysis and opinion
The urgent part is knowing where curl sits in each business, and that is not always obvious: it travels inside many programs that do not announce it, so checking the tool installed on a server is not enough. Software and device vendors need to be asked to confirm whether their products carry an affected version and when they will update it. The case also points to where open source security is heading: scanners backed by AI models are starting to find serious flaws in heavily reviewed projects, and that may bring more reports in a short time to small teams. curl's response, confirming the problem right away and bringing the release forward without skipping its procedures, is the good part. Patches arrive quickly, but they only protect those who install them.
Official source: curl · Written with the help of AI: how we make the news