Elastic unveils AlertZero, a team of AI agents for security teams
IA en un minuto newsroom · Editor: Jon Elgezabal
In 30 seconds
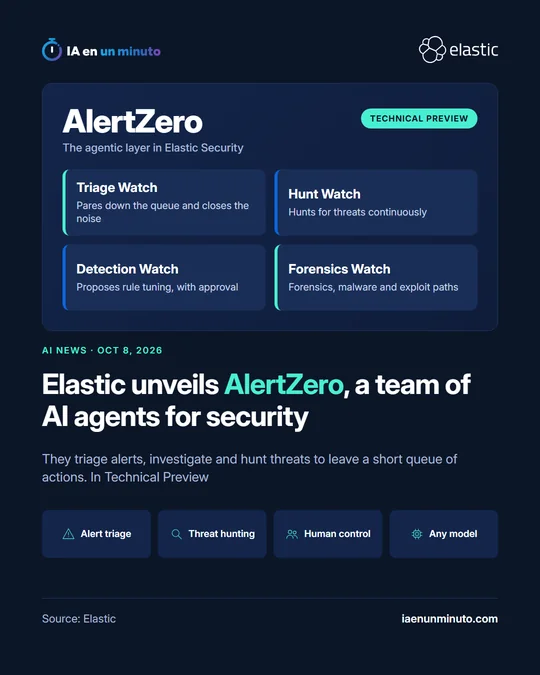
Elastic has added AlertZero to Elastic Security, a set of agents that filter and study alerts so the analyst is left with a few proposed actions. They split the work into Watches: one trims the queue, another tracks down threats, another suggests changes to rules and another does forensic analysis. It ships as a Technical Preview, accepts whichever model each customer prefers and has no date or price yet.
Elastic, the company behind Elasticsearch, has introduced AlertZero, an agentic layer built into Elastic Security, its security platform. They are specialized agents that learn from how each team already works and handle alert triage, investigation, threat hunting, detection tuning and forensic analysis, so each alert gets an evidence-backed answer.
Elastic frames the problem as one of volume: alerts have outpaced the analysts available to work through them, and false positives add to a queue that was already too large to clear. The goal is for analysts to move from thousands of raw alerts to a short queue of recommended actions, the equivalent of inbox zero. They decide which actions are automated and which are left to a person.
The work is organized into Watches, groups of agents with defined responsibilities that run on triggers and schedules. Triage Watch pares down the alert queue, closes the noise with a reason and escalates the real alerts. Hunt Watch keeps hunting for threats. Detection Watch proposes tuning for noisy rules and new rules for gaps, and it will not change a rule without approval. Forensics Watch adds depth in forensics, malware analysis and exploit paths. According to Mike Nichols, general manager of Security at Elastic, the level of autonomy can be customized for each Watch.
Elastic points to a recent case. In a high-profile attack, an autonomous AI agent generated more than 17,000 events across a production environment in only four days, moving from a dataset-pipeline exploit to credential theft and lateral movement (jumping from one system to another inside the network). The individual signals were detectable, but understanding the attack required connecting them.
AlertZero works with whichever AI model an organization chooses, in Elastic Cloud, self-managed or air-gapped deployments. It builds on existing Elastic Security capabilities such as Attack Discovery, Agent Builder and Elastic Workflows, and customers can extend it with those same tools, which Elastic used to build it. It will reach Elastic Security customers as a Technical Preview, and for now there is a form to receive updates. Elastic does not give a specific date or a price.
Why it matters · analysis and opinion
The bottleneck in security is often not detection but having enough hands to review what gets detected, and AlertZero goes straight at that: agents do the first pass and the final decision stays with a person. The delicate part is trust. An agent that closes a real alert by mistake does the same damage as a tired analyst, only faster, which is why two details of the announcement carry so much weight: every closure comes with a reason, and rules do not change without approval. For a small team that already works with Elastic, the preview is a chance to measure how many alerts it closes correctly before giving it more autonomy. Anyone on another platform can read it as a hint of where their vendors are heading.
Official source: Elastic · Written with the help of AI: how we make the news