A breach at Fireworks AI may have exposed Notion AI chats from under 1% of workspaces
IA en un minuto newsroom · Editor: Jon Elgezabal
In 30 seconds
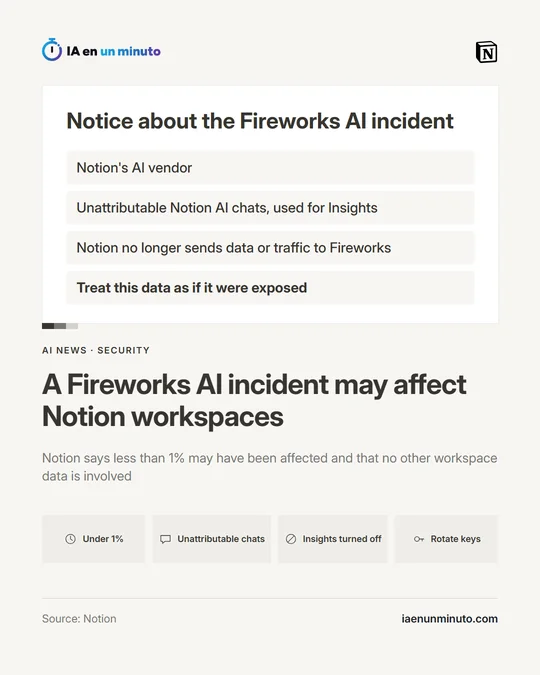
Fireworks AI, which provides AI services to Notion, suffered an intrusion that may have laid bare Notion AI chats with no name or workspace attached. The reach, according to Notion, stays below 1% of workspaces, and Insights is switched off while it investigates. Anyone who pasted passwords or API keys into those conversations should change them now, the company itself advises.
Notion has warned that a security incident at Fireworks AI, one of its AI infrastructure providers, may have affected under 1% of its workspaces.
What may have been exposed are some conversations with Notion AI that the company used for Insights, a feature that helps each customer understand how they use AI. According to Notion, these conversations were unattributed: they did not carry the name of whoever wrote them or the workspace they came from, and they did not include tool results either, such as the content of Notion pages or outside data brought in by the assistant. The company says no other workspace data is affected. Besides Insights, Notion relied on Fireworks to run open-weight models within its product.
Notion learned of the possible incidents early this month and, as of November 3, stopped sending data and traffic to Fireworks, disconnected its systems and deleted what it held there. On November 6, Fireworks told it that attackers might have reached customer data, and on November 8 it confirmed that new set of data. Insights remains switched off while the investigation continues. Notion has written to the owners of the affected workspaces, who can review that data from the sidebar; if they have heard nothing, it says, their workspace is not affected.
For its part, Fireworks explains that on October 24 an outsider without permission reached its development machines by exploiting an incident suffered the day before by a cloud provider that hosted them. The evidence points to a profit-driven cybercriminal group engaged in "LLMjacking": reselling stolen access to language models. Fireworks says it has not detected any further successful access since October 25.
Notion recommends treating that data as if it had been exposed and, if passwords, API keys or any other credential were pasted into the assistant at that time, changing them at once.
Why it matters · analysis and opinion
The case shows a risk that cannot be seen from the outside: what is typed into an AI assistant can end up processed by companies the user does not even know about. Notion was not attacked directly; a provider it sent conversations to for analysis was. The fact that those chats carry no name reduces the harm but does not remove it, because the text alone may contain recognisable details or secrets. The useful step is the one the company itself proposes: assume whatever was pasted is exposed and change any credential. From there, each team should be clear about what must never be pasted into a chat and should ask its tools which other companies handle that data.
Official source: Notion · Written with the help of AI: how we make the news